
The SOC Blind Spot: What Happens When Security Tools Become the Target?
When attackers target the systems designed to detect them, visibility itself becomes a security concern.
Security teams invest heavily in monitoring their environments. Endpoint agents are deployed, logs are collected, and security events are centralized in a SIEM. The assumption is simple: if something suspicious happens, the SOC will see it.
But what happens when the attacker targets the systems providing that visibility?
Security tools, logging infrastructure and monitoring agents have become part of the attack surface. An attacker with sufficient privileges may attempt to stop an agent, modify logging, change security policies or compromise the accounts that manage these systems.
The objective isn't always to disable security completely. Sometimes, reducing visibility is enough.
An attacker does not always need to defeat your defences. They may only need to make you see less.
Your Security Tools Are Part of the Attack Surface
Security infrastructure is trusted to monitor systems and enforce controls, which makes it valuable to attackers.
Consider a server that normally sends thousands of security events every day. If its security agent suddenly stops reporting, that change matters. The same applies when audit settings are modified, a logging service is stopped, or security configurations are changed unexpectedly.
None of these events automatically means an attack. Agents fail. Maintenance happens. Administrators make legitimate changes.
The problem is when the SOC cannot distinguish expected changes from suspicious ones.
This is why security monitoring needs to extend beyond the systems being protected. The tools responsible for collecting and reporting security information need to be monitored too.
Sometimes, Silence Is the Alert
Traditional detection focuses on what an attacker does: executing commands, creating accounts, moving laterally or accessing data.
A mature SOC also asks a different question:
What Are We No Longer Seeing?
At CyberSift, we have alerts in place to detect these visibility changes. This includes detecting offline agents and significant decreases in log counts from monitored sources, using machine learning to determine baselines based on hours and days of the week.

Liveliness section in Sentio
If an agent that normally reports continuously suddenly goes offline, that becomes an investigation point. Likewise, if a system's expected log volume drops significantly, the SOC can investigate whether the change is operational or whether something has affected the system's ability to generate or forward telemetry.
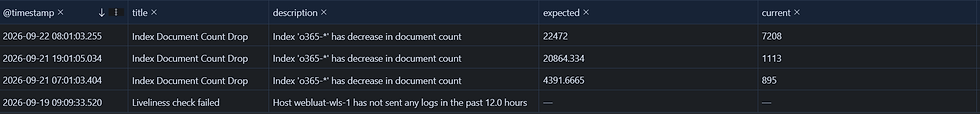
Example of alerts
These signals do not automatically indicate compromise. They provide an early indication that something has changed and give analysts an opportunity to investigate.
A mature SOC monitors not only the environment, but also its ability to see the environment.
This is where SIEM monitoring and threat hunting become important. By examining telemetry health alongside security events, analysts can determine whether a loss of visibility is an isolated technical issue or part of a wider sequence of suspicious activity.
For a deeper look at this approach, see Why SIEMs Need Strong Detection Engineering and How We Approach It at CyberSift.
Security Tools Need Security Too
Monitoring the health of security infrastructure is only one part of the problem. The systems and tools used to manage security also need protection against unauthorized access and changes.
At CyberSift, the in-house tools we provide to customers enforce multi-factor authentication and security auditing capabilities to help protect administrative access and identify activity that could indicate a potential compromise.
This creates another layer of visibility. Administrative actions and security-relevant changes can become investigation signals rather than remaining invisible to the SOC.
The principle is straightforward: the systems protecting your environment need to be protected with the same discipline as the environment itself.
Watch the Watchers
Security teams often measure visibility by how much data they collect. But volume alone does not guarantee that the right information is reaching the SOC.
A resilient monitoring strategy should continuously ask:
Are our security agents online?
Are expected log sources still reporting?
Has log volume changed unexpectedly?
Have security configurations been modified?
Who made those changes?
What happened immediately before and afterward?
This is where CyberSift’s SIEM, SENTIO, can provide value by bringing security events and telemetry together so changes in behaviour and visibility can be investigated in context.
The goal is not simply to collect more logs. It is to know when your ability to collect those logs changes.
If you cannot trust your visibility, you cannot confidently trust your detection.
Your security infrastructure is part of your security perimeter. Monitoring its health, protecting its administrative access and investigating unexpected changes can help close a blind spot attackers may otherwise exploit.
Learn how CyberSift SIEM and SOC Monitoring can help maintain visibility across your security environment.
-Written by Timothe Toulain
